The story in short
SherpaTech spend their days asking clients how well their data is protected. When they asked it of themselves, no one could answer it.
Most business leaders assume they know where their customer data lives. Then someone looks, and finds it scattered across old emails, personal drives and forgotten copies. That is what SherpaTech found in their own business.
SherpaTech is an insurance company based in North Sydney, NSW, providing professional indemnity, public and products liability, IT liability, and cyber insurance to businesses across Australia. The firm is backed by decades of combined insurance experience and is a member of NIBA, the National Insurance Brokers Association.
After partnering with FusionRed, the first step was not new software. It was a full data audit that showed exactly where their client information sat, including the places it should not have. From there FusionRed became the partner the previous providers never were: a documented plan, support that works around the team's schedule, and staff trained to spot and report threats.
The background
The firm that asks other businesses how they protect their data
When a business buys cyber insurance, it hands over a detailed picture of itself. Systems, exposures, financials, client lists. That information has to live somewhere.
SherpaTech holds exactly that for businesses across Australia. Their work is assessing how well other organisations manage cyber risk. That makes their own systems part of their product.
The challenge
They asked clients where their data lived. They could not answer it themselves.
The question SherpaTech puts to clients every day is a hard one to answer about yourself. The firm could not say with certainty where all of their client data sat. Their previous IT provider could not give a clear answer either. This was not negligence. The setup was never built to provide that kind of visibility in the first place.
Cybersecurity also sat outside the team's own expertise. They are insurance specialists, not security engineers. So the firm was in the position of asking clients how they protect their data while being unsure about their own.
Client data spread across emails, hidden OneDrive files and local copies
No documented record of where the firm's personal information lived
Previous providers without the security focus the business needed
The risk you cannot see is the one you cannot price
One mishandled record is enough to lose a client, trigger a privacy breach, or complicate your own renewal. Risk you have not documented is risk you cannot price. For a firm that prices risk for a living, that gap sat inside their own product.
Could you say where all of your client data sits right now?
Speak with our experts today →
In their words
“It was a really reassuring feeling to actually have a true audit of where we sat. I was most surprised by the sprawl of data in locations that I hadn't expected it to be. People emailing around spreadsheets, hidden OneDrive files, local copies of documents.

The solution
Fortify AssessThe first step was not new software. It was finding out what was already there.
Fortify Assess ran as a full data audit before anything was installed or changed. It mapped exactly where client information sat, including the places it should not have.
What it surfaced was sprawl. Client records were moving around in emailed spreadsheets, sitting in OneDrive folders nobody had catalogued, and duplicated as local copies on individual machines. None of it was deliberate. It had accumulated, unmeasured, over years of ordinary work.
For the first time, SherpaTech had a documented picture of their own exposure rather than an assumption about it.
Fixing how data is stored, not just where it sits today
An audit is a snapshot. The lasting change came through Fortify 360, FusionRed's fully managed IT and security service, which took over the day-to-day running of SherpaTech's environment:
- Data storage restructured, so new information lands in the right place and old copies get cleared instead of piling up
- Staff trained to spot and report threats, so security is not one person's responsibility
- Everyday logins simplified and secured, so the safer option is also the easier one
- Support available when the team is working, not only when someone is free
- A documented plan, so IT and compliance decisions are recorded rather than improvised
Want the same clarity over your own client data?
Speak with our experts today →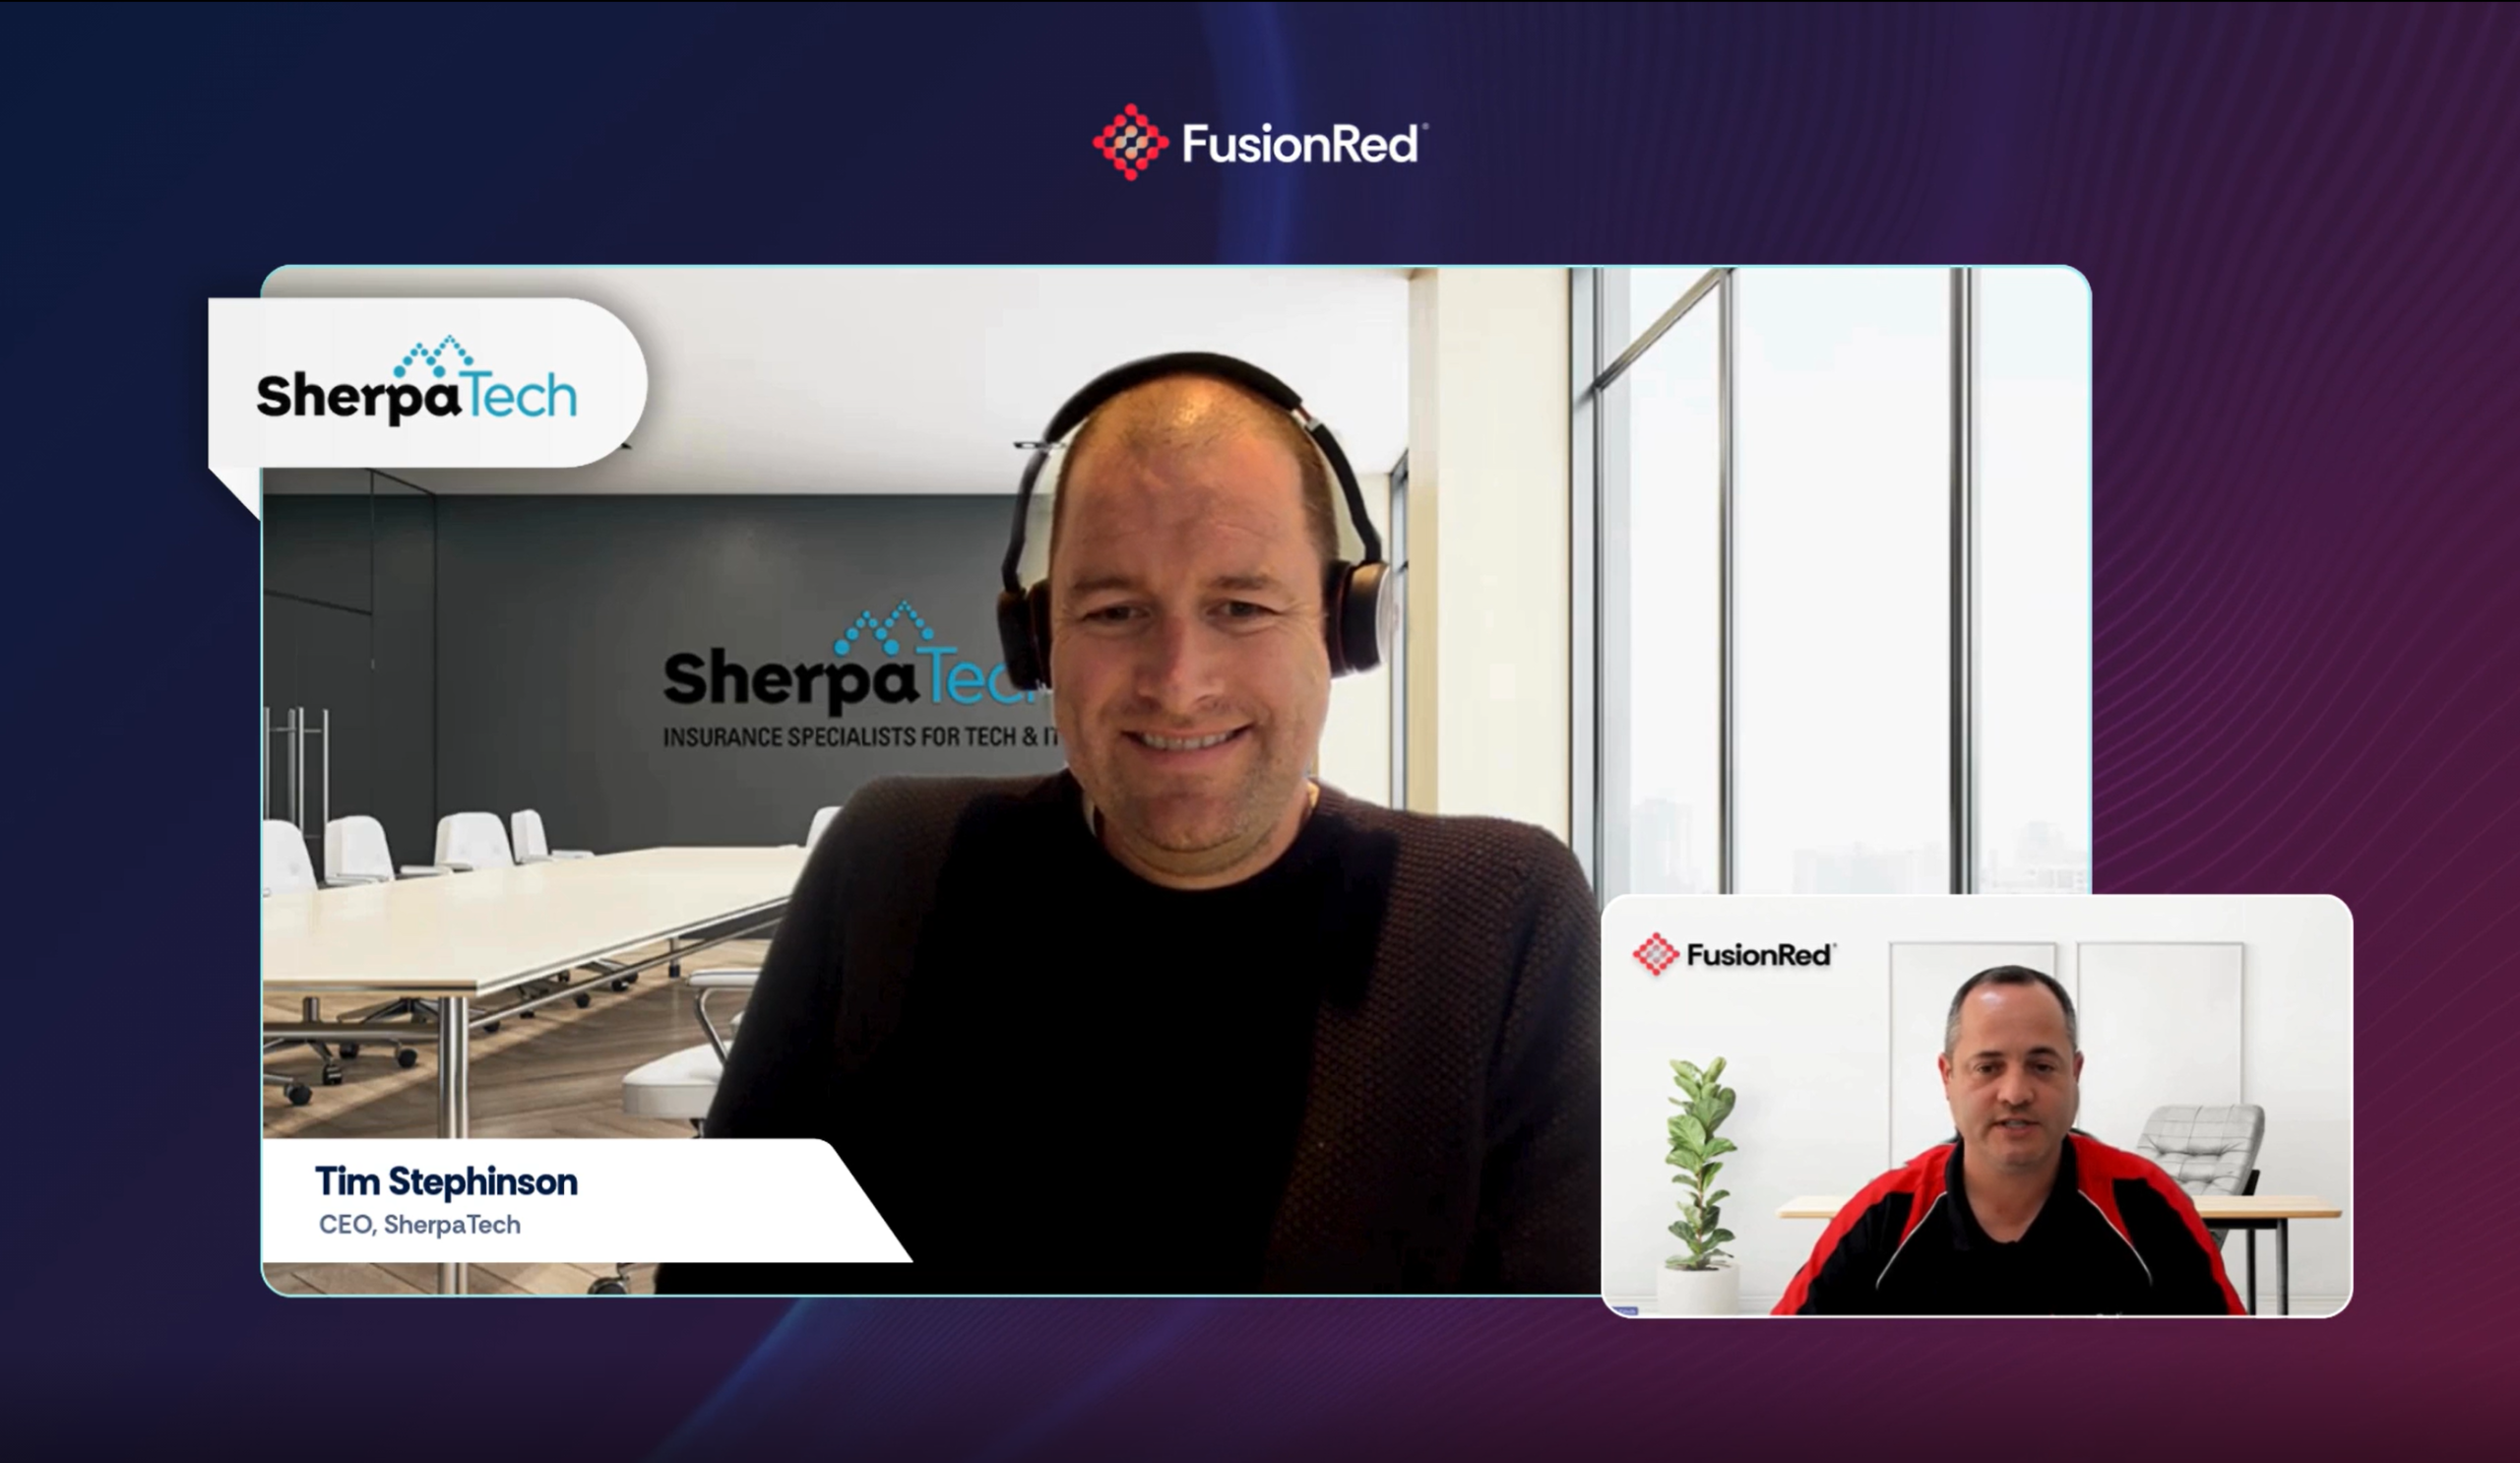
We just felt that the previous providers didn't really have the lens over security that we needed. When we can point to a partner like FusionRed that has set that up for us, they really are our internal IT team and compliance partner.Tim Stephinson · Insurance Broker and Specialist, SherpaTech
The transformation
A firm that can now answer its own question
The difference shows up in ordinary decisions.
- SherpaTech can name every place a client record lives
- Security is monitored and maintained, not assumed
- The team works through their systems, not around them
- Risk is documented rather than carried unseen
What this means for a firm whose product is risk
SherpaTech advises other businesses on cyber risk. They now run their own systems to the standard they ask of others. The advice and the practice match.
When an insurer or a client asks how their information is handled, SherpaTech answers with a document instead of an estimate. That is the difference between believing you are covered and being able to show it, and it is what lets the firm keep growing without wondering whether its systems will carry the load.
Start with knowing where your client data lives
You probably cannot say where all of your client data is stored right now. Most businesses cannot, until an auditor looks. Start with a data audit that shows you exactly what you are holding and where, so you can fix it before it becomes a problem.
and get a clear picture of where your client data actually lives.